This week, I had the opportunity to ask a room of 100+ CISOs at Black Hat to raise their hand if they could confidently tell me how many AI agents are running inside their company right now.
One hand went up. I said, "I want to talk to you after this." I couldn't find him after and couldn't sleep last night wondering if they raised their hand because the answer is an easy "zero" or because they have solved something no one else in the room had.
That moment encapsulated the whole week for me. Black Hat 2026 was agentic AI, top to bottom.
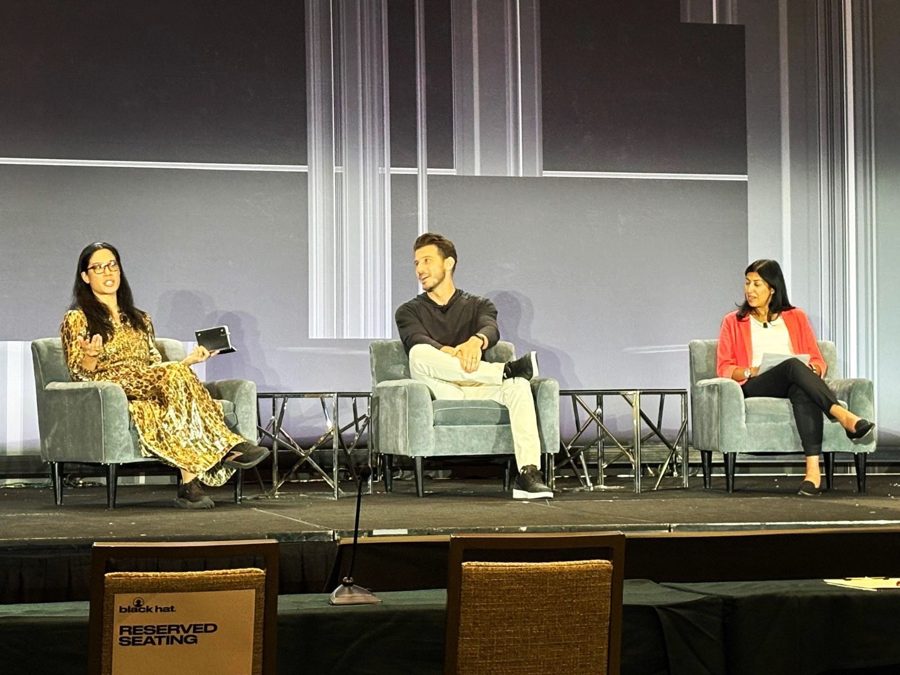
In my fireside chat with Avani D. and Caroline Wong, we got into an honest and respectful debate about where compliance audits stands today, and where the industry is headed because of AI. My bet is that the same continuous control monitoring that makes audit preparation faster and less painful will be table stakes in order to monitor AI agents over the coming year.
Then, in nearly every meeting with CISOs and partners, we talked about the same two themes: agent governance and third-party risk. Everyone needs to know what’s actually running inside the organization, but even more so, the conversation lands on a single question:
How do I govern AI agents without killing the very thing that makes them valuable --> their ability to decide and act on their own. That's the work ahead. And it's exactly what we're building at Drata.
I’m back home, but I can't stop thinking about the energy that surrounded me this week (and that one brave hand that went up!). Customers, partners, new faces, old friends… all in one place and all fired up about the same problem. I headed to Vegas excited to share what we’re doing. I left buzzing about all the potential ahead.
Best Black Hat yet, and we're just getting started. 🚀
Thank you to everyone who spent the week at the Drata booth demoing and speaking with so many visitors! Stefany Blinn Josh Schimpf Brayden Brookshier Collyn O'Brien Hailee Huffman Jackie Neilsen Brandon Kempf Dave Knell Dean Clark Rachel Khodursky Marcella Norris Johnny Kinder Jake C. Michael Goetz Jenna MJ Thomas, CCEP-I, LPEC David Aguiniga Habib Hourani 👏
After Black October, silence will be read as exposure.
Within six months, buyers will expect every vendor to share its status on a critical vulnerability within hours, and their TPRM agents will assess that risk in real time.
It's already starting. In the last 24 hours we've seen hundreds of Drata Trust Center updates about PHP2Shell alone, including our own. Customers, and their agents, wanted to immediately know if their vendors were exposed to the two critical flaws AI found in PHP, which runs roughly 70% of the web.
Anthropic's Deputy CISO Jason Clinton says things will get worse before getting better, and he's telling security leaders to go to their boards now for help with the basics. I agree, and I’d add that the basics have to run continuously.
What I'm hearing from CISOs this week:
- Patch windows are shrinking from weeks to hours
- Their vendors run PHP too, and they need to know which are still exposed
- AI agents are reaching production faster than teams can inventory them
- Annual reviews are a snapshot of a world that truly no longer exists
Continuous means knowing every system and vendor you depend on, AI agents included, and getting live evidence from vendors so you can answer "are we exposed?" the same day.
AI is accelerating the exposure we inherit and the exposure we create, and both now require trust that’s proven continuously. That's the problem we wake up every day building to solve, and it's a privilege to have that opportunity.
Starting today, we're making it even easier to launch your continuous security and compliance program with Drata.
🚀 Introducing Drata Academy
On-demand, self-serve training so customers and partners can learn at their own pace, launch their program faster, and keep their teams up to speed as they earn and maintain trust with all those they do business with.
This is something our customers have been asking for, and I'm very proud we're delivering it. With a lot more courses coming, this is just the start.
Special thanks to Kat Kenny for all of her hard work and ownership bringing this Academy to life, along with Molly Calhoun, William Reid von Gunten, Tamara Shoubber, Jacqueline Z., Shannon Trimble, Jade Hill, Ashley Hyman, Pilar Poeschl-Ellis, @Rose McGuigan, Liam Hession, Sierra Alvarez, all of our early access customers for your feedback, and the entire Drata team!
🎓 https://okt.to/cK1t0z
Third-party risk has become one of the most time-intensive jobs in security.
Vendor lists keep growing, and every vendor is now an AI vendor. Questionnaires pile up, and chasing a vendor for answers is slow work that carries a certain irony: "I'm going out of my way to help YOU sell to US." Even then, the review captures a single point in time. It tells you little about whether that vendor will still hold a strong security posture six months from now.
At Drata, we've spent more than five years helping thousands of customers continuously monitor the operating effectiveness of millions of controls. And with SafeBase (Acquired by Drata), we've built the world's largest network of enterprise trust centers, where vendors showcase and share that control information along with additional details of their security posture. This Trust Graph uniquely positions us to now solve the next dimension of trust for our customers in the AI era.
Today, I'm excited to launch Drata Third-Party Risk Management as a standalone, agentic solution:
✨ The agent applies your own natural-language standards to inherent risk, weighing multiple factors together in context, the way a practitioner actually assesses a vendor.
✨ The agent runs the security review end to end: syncing your vendors, tiering inherent risk, gathering and then assessing evidence against your criteria, and recording the decision. A human reviewer signs off on the result.
✨ Every assessment ships with the specific reasoning and evidence behind it. When an auditor or customer asks why a vendor was approved, you have concrete rationale to point to.
✨ The same standards apply to vendor #1 and vendor #1,000, removing the drift that comes from different reviewers, or the same reviewer on a different day.
We're replacing checkbox scoring with evidence-backed, defensible vendor risk decisions. What used to take days per vendor now takes minutes. The feedback has been terrific and the roadmap ahead is incredibly exciting!
More info in the comments. 👇