I read Dario Amodei's essay calling on the labs to pace the frontier. Sam Altman agreed. The frontier will move at whatever speed it moves. The rest of the world will not slow down. Our job in the cybersecurity community is to make sure it moves securely and safely.
Here’s what I see from the front lines:
1. The unit of threat is no longer the hacker. It's an autonomous campaign. I call it the Agent-state. We see coordinated AI agents executing attack campaigns at machine speed.
2. Sophistication is dead as an attribution signal. AI gives every criminal and lone actor elite execution. Identity, infrastructure, and intent tell you who's behind an attack. Skill doesn't.
3. Runtime is the control point. Endpoints, cloud workloads, and SaaS are the battleground. Governance documents don't stop an agent in motion. Enforcement at machine speed does.
4. Every AI agent is a privileged identity. Least privilege, short-lived credentials, traceable actions, and a kill switch. Permissions never expand because an agent decides it needs more.
5. Defense has to be autonomous but also bounded. Machine-speed response, tiered by consequence, with humans owning the high-impact calls.
6. Every failed attack should make every defender smarter. Feed what we block back into detection, across customers and models, with privacy intact. This is what CrowdStrike and NVIDIA introduced with SafeMind: an agentic, always improving model and harness protection system built for defenders.
7. The AI industrial base is critical infrastructure: weights, training clusters, APIs. Call it what it is and protect it like it is.
Pacing what comes next doesn't secure what's already here. The credible path is to deploy with proof: board-level accountability for AI security, independent external red teaming, incident disclosure, secure defaults, and controls that work in production - not on paper. Anthropic and OpenAI just committed to embedding independent evaluators with employee-level access. CrowdStrike will bring what we see from the front lines to that table.
The ability for AI to act must be matched by the ability for defensive AI to stop the breach.
https://lnkd.in/ggY5edWX
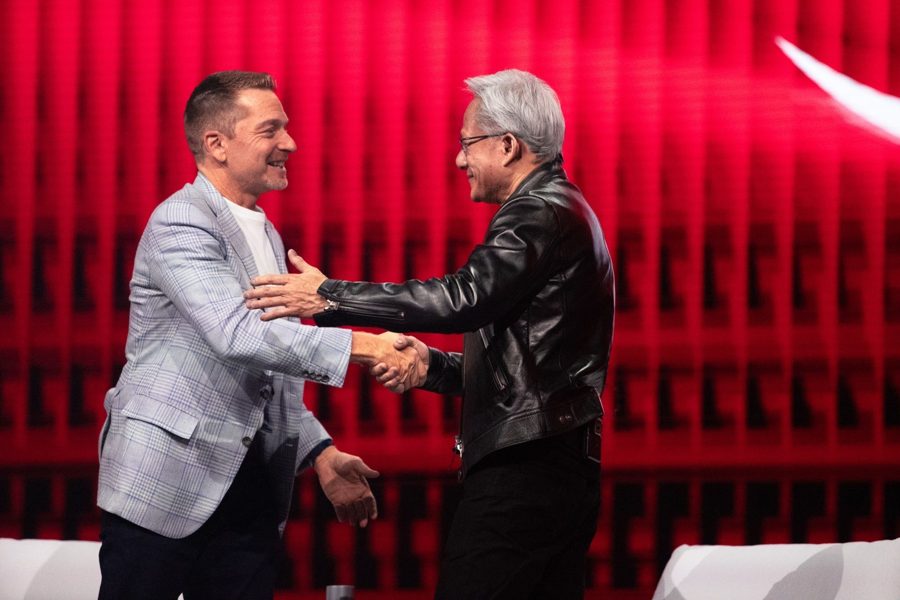
Thank you to NVIDIA’s Jensen Huang, Intel's Lip-Bu Tan, and OpenAI’s Greg Brockman for joining me at Fal.Con this week.
Together with NVIDIA, we post-trained Nemotron on fifteen years of Falcon attack data to deliver the world’s first frontier models and harnesses built for defenders. That's SafeMind. Lip-Bu made the case that security has to start at the chip. Greg talked about the window that defenders have right now to get ahead.
The crowd in CrowdStrike is the advantage. Thank you all for being part of it.
Last quarter we called it the Mythos moment: the inflection point where cybersecurity became an enabler for AI adoption. This quarter, inflection became acceleration.
📈 All-time record net new ARR of $333M, up 51% YoY, beating the high end of our guidance by $45M+
🔒 Ending ARR of $5.84B, accelerating to 25%+ YoY, our 4th straight quarter of accelerating growth
💰 Record Q2 free cash flow of $377M, up 33% YoY
⚡ All-time record non-GAAP operating income of $372M, up 46% YoY
🚀 All-time record Falcon Flex quarter: ending ARR surpassed $2.29B from accounts that have adopted Falcon Flex, up 101% YoY, with more new Flex accounts than the prior three quarters combined
AIDR ending ARR nearly tripled quarter over quarter. Enterprises are building with AI as fast as they're securing it, and standardizing on CrowdStrike.
That's why we raised full year net new ARR growth guidance again: 630 basis points this quarter at the midpoint, on top of last quarter's raise. Guiding up more than $100M above where we started the fiscal year.
To our customers and partners: thank you for trusting us with your security. To every CrowdStriker: relentless execution made this our best quarter ever. Thank you all. 🙏
Next week at Fal.Con in Las Vegas, I'll share where we're taking AI security next. See you there and join us on the livestream.
Full earnings release, including a discussion of risks related to forward-looking statements, and FY27 outlook at ir.crowdstrike.com.
The exposure management category is consolidating onto the Falcon platform.
Today CrowdStrike announced a definitive agreement to acquire the intellectual property of XM Cyber, a Schwarz Digits company, and to advance our partnership delivering the Falcon platform on the STACKIT sovereign cloud in Europe. European organizations shouldn't have to choose between security and digital sovereignty. They can have both.
I see security teams moving away from point product stitching. As frontier AI expands the attack surface, exposure management belongs on the platform - next to endpoint, identity, AIDR and cloud. I look forward to welcoming XM Cyber’s customers to the Falcon platform.
Thank you Gerd Chrzanowski and Christian Müller for your partnership and to the great teams on both sides that made this possible. 🙏
Press Release Here:
https://lnkd.in/gGNg7tgi
As defenders, you need to look at your watch, not a calendar.
PHP2Shell is a big one. Here are my takeaways.
1. These flaws reach back more than a decade. PHP’s maintainers identified one underlying problem in 2024, but its full impact wasn’t clear until AI-assisted research demonstrated its exploitability. What seems impractical to exploit today could easily be exploitable tomorrow as models advance.
2. Much of the web runs on PHP, and a lot of it is on versions that are out of support. Some get a source backport you must build yourself. Some get nothing. Attackers aren't hunting the servers you just patched. They're hunting the ones you forgot you own. There is going to be a very long tail on remediating these vulnerabilities, and we will see many downstream breaches over the coming months.
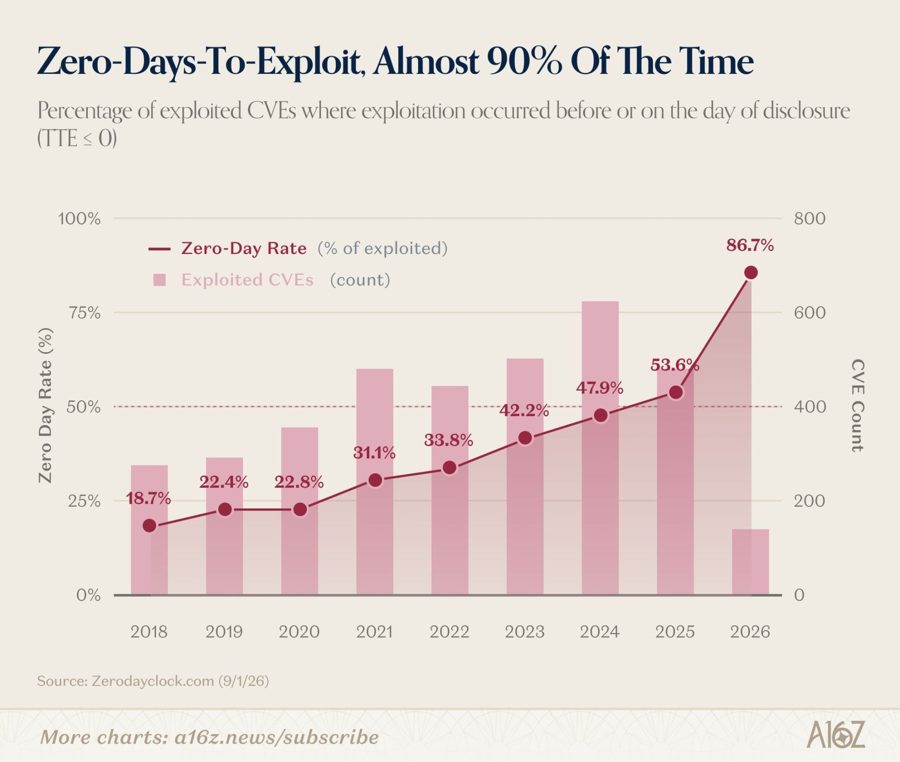
3. The patching window has completely collapsed. While we’ve exponentially found more vulnerabilities and exponentially created more patches, we’ve hit the sound barrier on operationally rolling them out. Even more concerning is the increase in exploitation occurring before or on the day of disclosure. When a flaw gets exploited, almost 90% of the time it’s hit on or before the day it’s disclosed.
4. Coordinated disclosure in open source is really hard. It runs on trust, not contracts. There were many people in the loop, and for good reason. Lots of great people doing incredible work. However, I expect leaked disclosures will be the norm, not the exception, as we move forward in the Agent-state era.
CrowdStrike has coverage in place to protect customers. Patching and upgrading vulnerable PHP versions should be the immediate priority.
https://lnkd.in/gsbDqirR
The Andreessen Horowitz chart below says it all.
It's always a highlight to talk with Jim Cramer about CrowdStrike's results, and there's never been more to talk about!
The adversaries aren't slowing down, and neither are we. We had a great conversation on where cybersecurity is headed and why the mission has never mattered more.
Full clip here:
https://lnkd.in/e_auMzna